AI for Business – The Risks, Benefits and How to Stay Protected
Artificial intelligence is already part of everyday work. It drafts emails, summarises meetings, compares documents and helps people clear routine tasks faster. Used well, it gives organisations time back for the work that needs human judgement.
Most organisations did not decide to adopt AI so much as watch it arrive, one helpful tool and one quick shortcut at a time. Structure has not always kept pace. National survey data points the same way, with governance and understanding of AI regulation trailing behind adoption.
That is why the most useful question is rarely which AI tool to choose. It is who has decided how AI is used in your organisation, what it can see and do, and who remains accountable for the outcome.
This guide covers the benefits of AI for business, the risks worth understanding and the practical steps that help organisations use AI with confidence. It also shows how CYAN uses AI ourselves, including how we tell you when it has helped shape something we give you.
What You’ll Learn

The Benefits of AI for Business
The benefits are greatest when they start from a real problem, such as where people lose time or why information is hard to find, rather than from a tool someone has seen demonstrated.
1. Boosting Productivity
Much of the working day follows a pattern: first drafts, summaries, reformatting data, checking a formula, turning a long document into something shorter. AI is good at that first pass, which makes it a sensible place to start.
In our own work, it helps with first drafts, summaries, data assembly and repetitive tasks.
It can also help with clarity. Text can be reworked for a different audience, or technical and legal wording turned into plain English for a proposal, policy or internal guide.
2. Improving Team Collaboration & Communication
In hybrid and fast-moving teams, useful information is easily lost between meetings, messages and inboxes. AI can summarise a discussion, pull out agreed actions and help people catch up on what they missed, so follow-up is quicker and fewer things fall through the gaps.
Meeting content often includes client or personal information, so which tool is used, and where that information goes, matters as much as the time saved.
3. Supporting Smarter Decision-Making
AI can help people reach relevant information faster by surfacing patterns in data, assembling figures for a report or laying out alternative angles before a discussion. That gives leaders a better starting point.
It does not replace the judgement. An AI output is a draft to question, not a conclusion to accept, and the person who uses it remains accountable for the decision that follows.
The Risks of AI in Business
AI is not one thing, and neither is its risk. A tool that helps tidy a public paragraph is very different from one that can read client records or update a live system. The more AI can see and do, and the more an organisation relies on what it produces, the more structure it needs around it. That level of risk also changes over time, as tools gain new features and connections.
None of these are a reason to prevent progress. They are the reason to put structure around how AI is used to support it.
Four risks come up most often.
1. Data Privacy & Confidentiality
Most data exposure from AI is not deliberate. Someone pastes in client case notes, a contract or a set of figures to get a task done quickly, using the tool closest to hand. This is often called Shadow AI: AI use the organisation has not approved or does not govern. It usually tells you that people see value in AI and have no clear route to use it properly.
The difficulty is control. A personal or free account sits outside any agreement the organisation can see. Once information is entered, the organisation cannot tell where it is stored, how long it is kept or whether it is used to improve the provider’s service, and it cannot have it removed.
2. Over-Reliance or Blind Trust
AI output is well structured, confident and quick, which can make it feel more reliable than it is. An analysis shapes a recommendation, the recommendation reaches a meeting or a report and the original output may never be questioned again. It can also carry bias or missing context that is hard to spot.
The risk is not that people use AI to help them work. It is that generated output starts to be treated as trusted judgement without enough challenge.
3. Ethical and Reputational Risk
Clients, employees and partners rarely judge the technology in isolation. They judge the organisation using it. If a report is wrong, it is the organisation’s report. If an AI-supported decision looks unfair, it is the organisation that must explain how it was reached.
That is why openness matters. Being able to say what was used, what it could see, who checked it and who decided keeps confidence intact when questions arrive. Where AI shapes content or influences decisions about people, fairness and transparency matter as much as accuracy.
4. When AI Can Act, Not Just Advise
A tool that simply drafts something still requires a person to review it before anything happens. A tool connected to other systems may update records, send communications or trigger workflows with far less review at each step. If the information it relies on is wrong, the mistake can become real before anyone notices.
Accountability stays with the organisation, whether a person or an automated process did the work.
The National Cyber Security Centre’s guidance on thinking carefully before adopting agentic AI is a useful starting point for any organisation considering tools that can act on its behalf.
How to Use AI Safely
AI is most useful when it sits inside the way an organisation already manages risk, security, data and accountability. It does not need a separate structure or a long list of restrictions.
These six steps give it a practical starting point.
1. Start with the work, and match the control to the risk
Begin with where people are actually losing time, then ask what data is involved, what the tool can see and do and what would happen if it got something wrong. A low-risk task using public information needs light rules and normal review. A system handling confidential data or influencing a decision needs more scrutiny.
2. Give AI governance an owner
Technical teams, security providers and advisers can support the process, but decisions about acceptable use, risk and accountability belong to the organisation. That does not need a new committee. It can sit across the leadership, risk, security, data protection, legal and operational responsibilities that already exist.
3. Approve tools and write the rules in plain language
Decide which AI tools are approved, make sure they are used through work accounts rather than personal or free ones, and be deliberate about settings and features that change what a tool can access. Then set data rules people will recognise, covering public, internal, personal and confidential information. Nothing sensitive should go into an AI tool without explicit approval. An AI policy explains these boundaries, and the technical environment should support them wherever it can.
4. Match human review to the consequence
A person should check AI output before it is relied on or sent on, and the person who approves it remains accountable for it. The depth of that check should reflect what is at stake. A public paragraph needs a light read. A client report, a figure or anything affecting an individual needs a closer one, including accuracy, confidentiality and any legal or intellectual property considerations.
5. Treat every integration and automated action as its own decision
Giving a tool access to other systems changes its risk, even though the tool looks the same. Look at what each connection can read and change, give people and tools only the access they need, and decide which actions can happen automatically and which still need a person. Keep a record of what the AI has done so that the organisation can understand it afterwards.
When we support AI tools such as Microsoft 365 Copilot for clients, we secure and configure the environment they run in and review data access and permissions before rollout. Decisions about how that organisation uses AI, what is acceptable and who is accountable remain theirs.
6. Make the safe route the easier one
People will find their own route if the approved one is unclear or slow. Give them a straightforward way to ask about a new tool or idea, and train them on the rules as they apply to their own roles.
What We’re Doing, What We’re Not Doing And How We Show It
At CYAN, AI helps our team to be more productive and deliver a better service. We adopt it deliberately, and people remain accountable for everything that reaches you. Our position is augmentation, not replacement: people set the task and make the judgement calls, and AI helps with the work in between.
Four controls apply every time AI is used in our work:
- Approved tools only. Every tool is risk-assessed and approved before use, and used only through work accounts, never personal or free ones.
- Your data protected. No sensitive or confidential information, including client information, goes into an AI tool without explicit approval, and approved tools must not train on our data.
- A person reviews. Someone checks AI output before it is relied on or sent to you. That person, their manager and ultimately CYAN’s leadership, remain accountable for it.
- Governed. AI sits within our ISO/IEC 27001 information security management system, with risk assessment, incident handling and regular review.
What we do not do matters just as much. We do not adopt AI faster than we can govern the data and systems it touches. We do not use it to replace our people, because lasting relationships are built person to person. We do not make decisions about people based solely on automated processing where those decisions have legal or similarly significant effects. Where AI is used in a decision that affects your contract, services or access, we tell you, and you can ask for a person to review it. And if AI would make your experience worse, we do not use it.
How you’ll know AI was involved
Where AI has meaningfully shaped something we give you, for example by drafting,
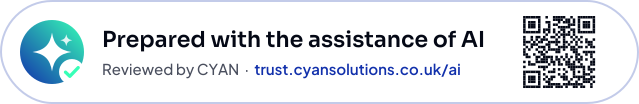
Because artificial intelligence tools helped prepare it, this article now carries the CYAN AI label, as will content from CYAN prepared in the future using these tools. It means three things:
- AI assisted. AI meaningfully shaped the content. Spelling and grammar tools do not count.
- Reviewed by CYAN. A named member of our team has reviewed it, corrected it where needed and approved it, and is accountable for it.
- Links back. The address takes you to our AI statement, so you can see how AI is used and governed.
We think this openness matters. A label like this turns a promise into something you can check: where AI helped, who stands behind the result and where to ask questions. It is a standard we would encourage any organisation to set for itself, including yours.
As a Certified B CorporationTM, we also look beyond security to fairness, transparency and client experience, and we review AI used in decision-making for bias.
AI in your own organisation
If you would like to see how this works in practice, read our AI statement or speak to our team about putting the right controls around AI in your own organisation.
If AI helped shape something in your organisation’s name this week, could you say where, and who stood behind it?
Updated October 2026 (Based on an article published June 2025)
Sources & Citations
Department for Science, Innovation and Technology. UK Business Data Survey 2026, Section 3: Artificial intelligence and data. GOV.UK, published 18 June 2026. https://www.gov.uk/government/statistics/uk-business-data-survey-2026/uk-business-data-survey-2026#artificial-intelligence-and-data
National Cyber Security Centre. Thinking carefully before adopting agentic AI. NCSC, May 2026. https://www.ncsc.gov.uk/blogs/thinking-carefully-before-adopting-agentic-ai
Further reading from CYAN
AI Organisational Readiness – Why Structure Must Come First. CYAN Solutions, 19 October 2026. https://cyansolutions.co.uk/cyan-ai-governance-in-practice-organisational-readiness/
Shadow AI Risks – When Good Intentions Create Real Risk. CYAN Solutions, 19 October 2026. https://cyansolutions.co.uk/cyan-ai-governance-in-practice-shadow-ai/
AI Governance First: What It Costs When It Comes Second. CYAN Solutions, 19 October 2026. https://cyansolutions.co.uk/cyan-ai-governance-in-practice-governance-first/
What Technical and Security Controls Should Organisations Put Around AI. CYAN Solutions, 19 October 2026. https://cyansolutions.co.uk/cyan-ai-governance-in-practice-technical-security/
Who Owns AI Governance? – Making It Part of Everyday Work. CYAN Solutions, 19 October 2026. https://cyansolutions.co.uk/cyan-ai-governance-in-practice-governance-together/